
- Coinbase reported no evidence of unauthorized access to its own systems.
- Coinbase says a breach at third-party analytics provider Amplitude exposed contact information of a small subset of customers.
- SlowMist’s 23pds claimed more than 70,000 users were affected, but Coinbase has not verified the figure. Customer funds remain unaffected, according to the exchange.
Major cryptocurrency exchange Coinbase has pushed back against claims that its own infrastructure suffered a security breach, clarifying instead that a third-party analytics vendor, Amplitude, experienced an incident that compromised the contact details of a limited number of Coinbase users.
Via its official support account on X on October 28, the cryptocurrency platform explained that the event impacted a small subset of Coinbase customer contact data, alongside data tied to other businesses that utilize Amplitude.
Coinbase emphasized that it discovered “no evidence of unauthorized access” targeting its proprietary systems and verified that user funds stayed completely secure. The exchange also noted that it is reaching out to affected clients and relevant regulatory bodies as required by law.
Coinbase has not had a data breach.
Amplitude, an analytics vendor, experienced a security incident which impacted a small subset of Coinbase customer contact data, among other Amplitude customers.
We’ve found no evidence of unauthorized access to Coinbase systems, and customer funds were not impacted.
We are notifying impacted customers and regulatory agencies in accordance with our legal obligations.— Coinbase Support (@CoinbaseSupport) October 28, 2026
The enterprise has withheld the precise tally of impacted customers and has not shared a comprehensive inventory of the exposed data fields.
70,000 Coinbase Users Allegedly Affected, but Figure Remains Unverified
This response came on the heels of online reports suggesting that malicious actors had secured contact details for over 70,000 Coinbase accounts. That statistic stemmed from a social media statement by 23pds, who serves as the chief information security officer at blockchain security enterprise SlowMist.
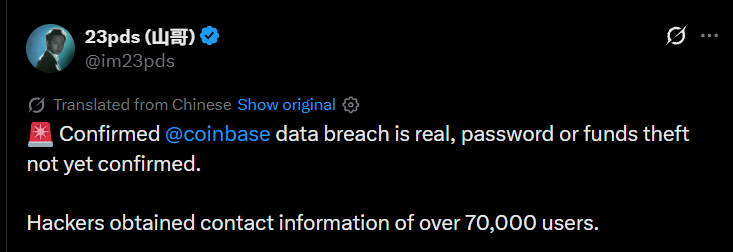
Nonetheless, Coinbase has not authenticated this number, maintaining in its official communication that the impacted demographic constitutes just a “small subset” of its user base.
Amplitude offers analytics solutions designed to help businesses track user interaction across apps and websites. Consequently, security breaches at external vendors can compromise consumer data even when the primary enterprise’s network defenses remain intact.
Exposing contact information often paves the way for phishing schemes and social engineering attacks, wherein bad actors masquerade as exchange representatives to manipulate users into handing over login credentials or security verification codes.
Coinbase has confirmed that client assets experienced no disruption. Furthermore, there is zero verified proof that the breach granted intruders entry into its core network architecture.
The full scope of the data exposure is still undefined while the exchange persists in alerting impacted patrons and coordinating with regulators. Additional specifics, such as the exact volume of individuals impacted and the precise data elements leaked, have not yet been made public.
Frequently Asked Questions
Did Coinbase experience a direct data breach?
No. Coinbase reported no evidence of unauthorized access to its own systems. The security incident occurred at a third-party analytics provider, Amplitude.
Are customer funds safe?
Yes. Coinbase confirmed that customer funds were not impacted by the incident.
How many users were affected?
Coinbase described the affected group as a “small subset” of its customers and has not verified online claims that more than 70,000 users were involved.
What data was exposed?
The incident exposed a small subset of Coinbase customer contact data, though a complete breakdown of the exposed information has not been disclosed.
